

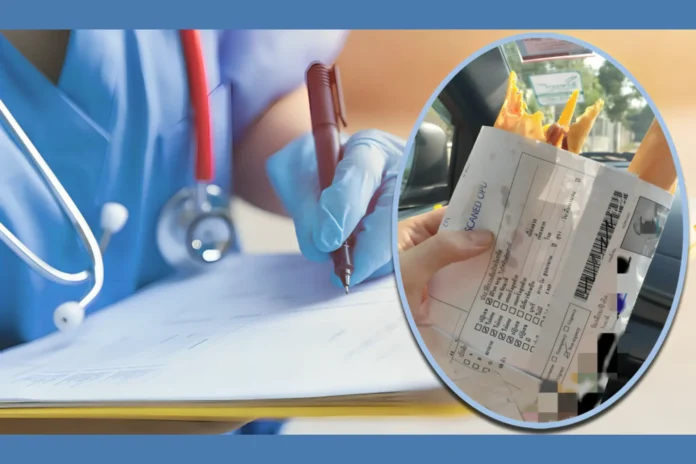
On a boiling Ubon Ratchathani afternoon, a street food seller gave a customer a crispy khanom Tokyo, a favorite Thai crepe-like treat. But rather than wax paper or plastic wrap, the snack was packaged in a sheet with a patient’s hepatitis B diagnosis printed on it, along with a name and an ID number.
This bizarre moment initiated the start of one of Thailand’s most egregious privacy invasions in recent times. What initially started off as an anomaly posted on a Thai influencer’s Instagram soon became a national embarrassment with deep implications for the nation’s management of sensitive health information.
It all started in May 2024, when popular Thai influencer “Dr. Lab Panda” shared a photo of the medical-record-wrapped khanom Tokyo to social media. The image ignited a firestorm, amassing more than 33,000 reactions and 1,700 shares. At first, the public assumed it was a one-off mistake. But soon, it became clear this was just the surface of a larger issue.
A tweet from X.
Over 1,000 pages of confidential hospital records, including personal identifiers and diagnosis details, had been improperly used as food wrappers in Ubon Ratchathani’s street food stalls.
“It was disturbing,”
the influencer later told followers.
“You don’t expect to see someone’s entire medical history next to your dessert.”
The hospital responsible still unnamed publicly had outsourced the destruction of patient records to a small, family-run disposal firm. Instead of shredding the documents, the contractor stored them at home and later sold them off as scrap paper.
This blatant mishandling of personal health data violated Thailand’s Personal Data Protection Act (PDPA) a law modeled in part on the EU’s General Data Protection Regulation (GDPR) and the U.S. Health Insurance Portability and Accountability Act (HIPAA). Under Section 26, health data is considered highly sensitive, requiring strict protection, especially during disposal.
On August 1, 2025, the Personal Data Protection Committee (PDPC) concluded its investigation and issued fines:
1.21 million baht (≈ US$37,000) to the hospital, as the data controller
16,940 baht (≈ US$520) to the disposal contractor, as the data processor
The PDPC cited a
“failure to supervise third-party vendors and gross negligence in handling sensitive personal data.”
The PDPC’s response is part of a broader crackdown on digital negligence. Since 2024, it has issued over 21.5 million baht in fines across six major breach cases including a state agency cyberattack that exposed data of over 200,000 Thai citizens.
Thailand’s data protection system is yet growing. Although the PDPA provides a similar structure like the GDPR, it is criticized for being reactive rather than preventive in enforcement. This hospital data breach highlighted systemic weaknesses in particular: poor contractor supervision, insufficient destruction procedures, and antiquated paper-based recordkeeping.
